Showing posts with label view. Show all posts

Tuesday, July 31

Don't: Using vC SQL Express as View's Event database

Now this shall be used as demo/lab only. Express is a toy anyway.
I used vC 5.0 and View 5.1 - versions apply.
To use vCenter's stock installed SQL Express as the Events database of View, do the following steps:

  • Setup mixed mode authentication and a user/DB in the SQL Express:
    • Download & install SQL Server 2008 Management Studio Express on the VC. This blog post may help.
    • Login using Windows authentication.The server name can be "." or localhost...
    • Right-click on the top of the tree (SQL server), choose properties. Choose "SQL Server and Windows Authentication mode" on the Security tab. OK.
    • Open Securty/Logins in the tree. Right click on Logins, New Login.
    • Setup a new user. Make sure it's using SQL Server authentication.
    • Right-click on Databases. Create a New Database. It's owner should be the newly created user from above. You can now exit the whole thing.
  • Open SQL server configuration manager. Choose SQL Server Network Configuration. Click on Protocols for VIM_SQLEXP. Right-click on TCP/IP. Properties.
  • Make sure General is enabled on the Protocol tab (should be). Set enabled and active to yes on the IP (IP Addresses tab) that View will use to communicate. Clear out TCP dynamic ports setting everywhere - no 0 or anything in them. Set IPAll TCP Port to 1433. Apply & close.
  • Open TCP port 1433 on the firewall for connections, just in case ;)
  • Reboot or restart SQL and VC services by hand.
  • You can check the SQL is listening on TCP 1433 by issuing the command "netstat -an -p TCP" in a command prompt, and looking for the line "TCP 0.0.0.0:1433 0.0.0.0:0 LISTENING"
After this, you can connect the Events database from the View administrator to this SQLe. You can check "%programdata%\VMware\VDM\logs" on the view server for any errors.

Friday, July 20

vCenter 5.0 & View 5.1 Certificate extravaganza - the OpenSSL way

With the release of View 5.1, VMware got strict on forcing people to be more secure. When installing 5.1, you have to make the view server fully trust in vCenter's own certificate, let it be a self signed or a real one. Now, getting a real certificate shouldn't be much trouble, or, if you are (or have) a demanding AD administrator, you should already have an own root certificate pushed by domain policies. In this case, you can quit reading this article.
If you don't have one, you could still make View to believe in vCenter's own certificate, accepting it's thumbprint.
For a more demanding solution, you could generate a root certificate (own CA), distribute it with an AD policy and chain vCenter's and View's certificates after it. That's more serious business.
We'll do this with OpenSSL now, of course MS CA services could be used as well.
  1. First, download OpenSSL (apt-get or yum it, or here it is for windows).
  2. Generate a new key file, this will be used everywhere: openssl genrsa -out rui.key 1024 - we don't encrypt it on purpose.
  3. Generate a new root certificate (CA): openssl req -new -x509 -extensions v3_ca -key rui.key -out myroot.crt -days 3650 -config openssl.cnf
  4. How do you make these things larger?
  5. Bind the generated root certificate (myroot.crt in the above example) to a Domain Policy. Put it in the  Trusted Root Certification Authorities container, to have it pushed to all domain member computers (see this MS TechNet article, this is called gpmc.msc). Use gpupdate after that for a policy refresh on Windows machines (even on the DC!). This makes our root CA to be trusted on all domain computers. You can use certmgr.msc on domain members to check if the push was successful.
After this step, you shall have a trusted, domain wide root CA for yourself. Now we should start making special certificates for vCenter, View & any other host that needs one. For vCenter (on Windows platform):
  1. Generate a new certificate request (there is a whole lot of material about vCenter & certificates on the web, see this kb, or this, even this excellent blog post collection): openssl req -new -key rui.key -out rui.csr -config openssl.cnf - Remember, Common Name wants to have the FQDN of the machine the certificate will be used on (i.e. vcenter1.yourdomain.com).
  2. (Optional) If you want to make it really choosy, you can create a new file (ext.txt) that tells OpenSSL,that this key will only be used for Server Authentication, has a CRL and can serve multiple domain names. The file shall include these lines:
    extendedKeyUsage=serverAuth - limit cert usage
    crlDistributionPoints=URI:<http://someserver/mycrl> - link to CRL
    subjectAltName=DNS:<FQDN1>,DNS:<FQDN2>,DNS:<etc> - aliases
    Please note that, that I did not create a CRL file, so if you want to use one, you'll have to dig yourself into the <openssl ca> commands.
  3. Sign the request with the Root CA: openssl x509 -req -in rui.csr -CA myroot.crt -CAkey rui.key -CAcreateserial -out rui.crt -days 3650 <-extfile ext.txt> - The last parameter is only required if step 2 was done.
  4. Export the signed vCenter certificate into PKCS12: openssl pkcs12 -export -in rui.crt -inkey rui.key -name rui -passout pass:testpassword -out rui.pfx - testpassword must be used, if you don't want to fall into the vpxd -p trap.
  5. Copy over the newly generated files rui.key, rui.crt & rui.pfx onto your vCenter's C:\ProgramData\VMware\VMware VirtualCenter\SSL directory. Back up the 3 files there before overwriting.
  6. On your vCenter, navigate to http://localhost/mob/?moid=vpxd-securitymanager&vmodl=1, login with a vC administrator, click reloadSslCertificate then Invoke Method. If you see Result: void, then you're done! Based on VMware KB #2009857.
Congratulations! You have a distributed CA and a vCenter that's using the cert chain.


As stated in VMware View 5.1 Installation guide on page 81, View will always try to check for revoked certs, and automatically won't trust any cert, that does not have a CRL linked or it's revocation URL can not be reached. To circumvent the extreme paranoid behaviour, there is a registry switch to turn this off (if you did not take the optional step, you'll need this).
Fire regedit on the View server, then create a string named "CertificateRevocationCheckType" under "HKLM\Software\VMware, Inc.\VMware VDM\Security" and set it's value to 1.
If you add your vCenter now, it's certificate shall be accepted without hassle.

But if you want to make View trust in itself (no red square on the dashboard for the connection servers in View Administrator), you still have to replace it's certificate too:
  1. Generate a request for the View cert: openssl req -new -key rui.key -out view.csr -config openssl.cnf. As before, use FQDN as the Common Name.
  2. (Optional) You can modify ext.txt if you created and used it as above.
  3. Sign the csr: openssl x509 -req -in view.csr -CA myroot.crt -CAkey rui.key -out view.crt -days 3650 <-extfile ext.txt>
  4. Export PKCS12: openssl pkcs12 -export -in view.crt -inkey rui.key -name vdm -passout pass: -out view.pfx
  5. From here, see the View 5.1 Install guide pg. 75-77. Digested below:
  6. Open the Local Computer Certificates on the View server. Run mmc, click on File->Add/Remove Snap-in..., click on Certificates, Add. Choose Computer Account->Next->Local Computer->Finish. Press OK.
  7. Expand Certificates->Personal->Certificates. You shall see View's default generated certificate here. First, right-click on it, choose Properties. Change it's Friendly name to something. Press OK.
  8. Right-click on the lower Certificates item, choose All-Tasks->Import...
  9. Browse for view.pfx. It's password shall be empty. Enable the Mark this key as exportable checkbox! Next-next-finish.
  10. The new key's Friendly name shall already be set to vdm, because of the PKCS12 export parameter -name, but double check it.
  11. Stop and start the VMware View Connection Server service (wait for all depending services to stop) or reboot the computer (it is a windows after all).
After login, another nice green square shall await you. What a reward...
If you gone this far, than you probably already hate SSL Certificates. At least I did. Sorry for the long post. Over & out.

Sunday, July 15

VMware View 5.1 - changing vCenter's address in the ADAM

So, if you have a View 5.1 (possibly upgraded from 4.x or 5.0) server, sometimes you are in the not-so-enviable position of having a vCenter registered by IP address, and unable to change it or remove it because of a certificate mismatch - you can't even validate a normal certificate for an IP. In this case, you can start deep diving into ADAM - The Active Directory Application Mode - the own embedded LDAP/AD service of View.
Here is where to change a registered vCenter's address inside View, without any impact on the pools, etc.
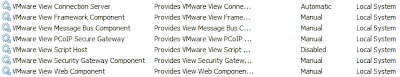
  • First, you have to stop all services of View on it's own server. These should be everything that starts with VMware View in services.msc:
  • See this VMware KB about how to connect to ADAM.
  • Choose OU=Properties -> OU=VirtualCenter in the tree.
  • There can be several Common Names at this point, all referring to the Virtual Centers that are connected to View.
  • Right click on any CN to investigate it's properties. The attribute named pae-VCURL holds the address of the particular vCenter, that View is using to reach it. You have to change it only here.
View keeps virtually everything in ADAM, so in rare cases you will have to hunt in it for a particular setting. I recommend reading this KB about orphaned linked clones too. Now it may look old, but who knows when you have to use it with 5.1?
Also, if you want to revoke your trust in this VC's self-signed cert, you can simply clear the pae-VCSslCertThumbprint & pae-VCSslCertThumbprintAlgorithm attributes. Use the clear button to revert them to  of course.
That is all, go and explore ADAM on your own. Don't forget to ruin some enterprise system also.

Friday, April 15

Bandwidth requirement of the Teradici HW Zeros

I was planning a View infrastructure based on HW Teradici clients, over WAN.
I found this document about the HW Tera clients, which is for PCoIP host cards and zeros, but it applies for zeros and View 4.6 too. The facts:
  • The minimum bandwidth for a Teradici based Zero (see previous post and list of devices) is about 1 Mbps. This is the "bandwidth floor" in the firmware settings. Using a Cisco 6500 we limited the effective bandwidth in Layer 2 for the device (Samsung NC190 and NC240, tested separately). We found out, that the client becomes "sluggish" at about 512 Kbps, and the whole session is unusable/unstable below 256 Kbps. This is not a limitation of PCoIP, because it is known to work at about 150 Kbps. It's probably a limitation of the TERA1x00 chip.
  • The maximum bandwidth usage as stated in the document above, is 220 Mbps. I can hardly believe that the device can use this much, but who knows. Watching HD video/audio on a dual 24" screen setup, while scanning and copying files over USB probably peaks way above 100 Mbps. The 220 Mpbs theoretical maximum is probably counted with 4 24" monitors daisy chained over 1 Tera chip, with HD audio and video streams and heavy USB usage.
  • The average usage that we observed while clicking MS word and such on the 24" (resolution counts bandwidth of course) was about 6-7 Mbps with a minimum usage just above 1 Mbps and maximum peaks at about 13.
Conclusion? The HW Tera devices are not fitted for low bandwidth situations, while they are probably the best technology if You happen to have enough bandwidth/device.
I will try out PCoIP software clients (Windows & HP's Linux one :)) in the near future with the same bandwidths.

Monday, April 11

The dark truth

Today we learned that Quickprep does not generate a new machine SID (Yes, it IS in the manual), so quickprep'ing 25 VM's won't activate a KMS server. Nice, I had to create a Sysprep'd pool just to trigger KMS...
The worse thing, that sometimes recomposing simply fails because of some kind of AD error etc.
If this happens, You've to manually clean out the failed VM. This is tricky, see http://kb.vmware.com/kb/1008658. You have to run a SviConfig -operation=removesviclone command on the view composer (vCenter) machine, and manually remove the ADAM CN from the View manager. This is done in ADSI edit, as stated in the KB above.
The trick is, sometimes this is not enough. Looks like the clone vanished, in AD Users and Computers mmc snap-in You don't see the incriminated computer's name, but View manager fails to create the VM again, because it still sees it in AD ("A computer with the name xxx already exists in Active Directory.") . Now, this happens when AD does not really delete the computer's account. To circumvent this, You manually recreate a computer account name with the same name as the VM, and delete it again...
Sorry, late night post.

Friday, April 8

The Linux PCoIP client from HP

There was some hassle about VMware's support for View client on Linux.
The official way to access View from linux is using view open client from http://code.google.com/p/vmware-view-open-client/. Now, this client does NOT support PCoIP, which is a major drawback.
You can access View using PCoIP from your Windows, iPad, or Teradici based device (I prefer Samsung's NC series, but the Wyse P20, the Dell FX100 etc are all the same. A complete list of devices using Teradici's HW is available here).
Android or iOS on the phone are not supported (yet). There is the Wyse PocketCloud, which is a great thing, but for RDP only.
So HP developed it's own version of View client for Linux, the code is probably heavily based on the open client (it uses the same interface, same config files/options...).
This software is for HP's thin clients with a kind of debian based firmware, but luckily it is a simple i386 .deb package.
One can easily download it from HP's site, and use it for his own dark purposes, as stated in this forum thread.
Currently, there is a View 4.5 based client in it, which works as charm with 4.6.
To download the archive, go to HP t5545 Thin Client support (search for the device on HP.com, then choose support), and download the link HP ThinPro Add-On (VMware View Broker) / 4.5.0-293049-1 Rev. A - 12 nov. 2010 - 5.2 Megs. The file is called sp50874.exe. Okay, for lazy people, it is here :) ftp://ftp.hp.com/pub/softpaq/sp50501-51000/sp50874.exe. It will extract a few files to C:\Program Files\Hewlett-Packard\HP ThinPro\3.2\Add-On\View45 by default. We will only need vmware-view-client_4.5.0-293049-1_i386.deb.
If you don't have dpkg (slackware ftw), then simply rename the .deb to whatever.ar, and ar x it. Then in the data.tar.gz you will find the required directory structure.
For 64biters: this will require 32 bit versions of libxml2.so.2 and libpixman-1.so.0, in /usr/lib.
To use USB redirection, there is postinst script in control.tar.gz, that will do the trick.

Tuesday, April 5

PCoIP Secure GW - this sh*t works

After some hassle, the new View 4.6 Secure Gateway finally works with PCoIP connections too.
The symptom was simple: PCoIP connections disconnected immediately, while RDP connections did work. I didn't find any log in C:\ProgramData\VMware\VDM\Logs that would hold any information about the disconnects, alll log entries were the same for the PCoIP and the RDP sessions.
I read markbenson's doc at the communities site, and found out that I forgot to check the checkbox on the view connection server administration site to enable the PCoIP on proxied (gateway'd) connections.
This one:

Now I only have 2 concerns.


In the Debug log there is a Java socket error, about some Tunnel IO problem. At first I thought it was some routing/firewall issue, because the SecGW is in a DMZ of course. I think this happens every time, when a client disconnects:
 DEBUG [ab] (4B412F31EACA3A955A8CDB2CBCC06EF6) Tunnel IO problem: java.io.IOException: Bad length com.vmware.vdi.ob.tunnelservice.ab.run(SourceFile:892)
java.io.IOException: Bad length
at simple.http.ChunkedInputStream.doLength(ChunkedInputStream.java:334)
at simple.http.ChunkedInputStream.nextChunk(ChunkedInputStream.java:266)
at simple.http.ChunkedInputStream.parseRead(ChunkedInputStream.java:250)
at simple.http.ChunkedInputStream.readBytes(ChunkedInputStream.java:181)
at simple.http.MonitoredInputStream.read(MonitoredInputStream.java:115)
at java.io.DataInputStream.read(DataInputStream.java:132)
at java.io.BufferedInputStream.fill(BufferedInputStream.java:218)
at java.io.BufferedInputStream.read(BufferedInputStream.java:237)
at com.vmware.vdi.ob.tunnelservice.df.b(SourceFile:1022)
at com.vmware.vdi.ob.tunnelservice.ab.run(SourceFile:763)
at java.lang.Thread.run(Thread.java:619)
This could be anything from a bug in some java code to "working as intended" speeches.


My other thingie is interesting too. Even with 8GBs of RAM, the Security Gateway installation cries for more memory on Win2008R2 SecGW VM:


Of course I did not find any infomation in the View administration Guide regarding the sizing of security servers. Will look it through again sometime.

Monday, March 21

VMware View and Windows 7 WGA / WAT

Wow. I haven't write a single line since a few months. Been busy I guess.
So. Currently I am playing with View 4.6 (and some other things covered by NDA :))
The worst part about creating a windows pool currently is Windows Genuine Advantage or Windows Activation Technologies. You have basically 4 ways of getting an activated - Windows 7 - pool:
  • MAK - Multiple Activation Key. This Works, but You are slowly killing Your key counter every time You provision a new desktop.
  • KMS - Key Management Server. The preferred way both by MS and VMware. We'll see this one below.
  • OEM Image - With some BIOS hacks (I am not sure of this one), You probably can install a Win7 OEM that won't kill activation after a QuickPrep/Sysprep.
  • Some nicely "prepared" windows, for example with ChewWGA. We should not speak about this :)
About the KMS part. You have to install a KMS key on a Windows computer to use this. See MS Technet articles at http://technet.microsoft.com/en-us/library/ff793419.aspx. About it's not so rare faults, You can read at http://support.microsoft.com/kb/938450. There is a big limitation about KMS, that affects VMware View: You have to install/provision at least 25 Desktops (Vista or 7), to have the KMS activate them. The number of desktops waiting to be activated can be queried with slmgr.vbs -dli. This causes error 0xC004F038, the one I found most annoying. It means, that You don't (yet) have the required number of desktops (>=25), to have them activated by Your KMS service. If You try to just provision 10 for example using Quickprep, they will fail to leave Customizing state and enter Available state.
This happens, because QuickPrep, by default, tries to KMS activate after changing the SID, and will get into a 10 minutes retrying loop if slmgr service on the cloned desktop encounters the error mentioned above. If You provision at least 25 at once - first time speaking of course - this won't happen.
To circumvent this failure of QuickPrep, VMware distributed a Knowledge Base article: kb.vmware.com/kb/1026556. It says You can disable the KMS activation part of QuickPrep, and skip activation completely, or do MAK for the slowly killing thing. The windows will try to activate itself of course, but at least will be in available state in the View Manager. After You have this, You can KMS activate Office 2010 too, a nice howto is at blogs.technet.com. If You setup the KMS server to know about office too (1meg patch, here), it will work automatically.
That's all folks...

Monday, May 24

Backfire

I set up Openwrt 10 "Backfire" today. I needed iodine, and my old Whiterussian got that crippled. After that I had to put "iptables -A forward -i dns0 -j zone_lan_forward" in /etc/firewall.user so I can use the local end of the tunnel as a gateway, not just lousy socks proxying over ssh (which is on port 443 of course - not working with ISA).
I need these tricks sometime to use Internet (to read documentation :)) from some clients' datacenter rooms, where is no 3G or proxy access.
I managed to get a sneak-peek on the upcoming vSphere releases and View 4.5. Tough NDA-s (I  might get castrated if I gossip), but I must say I like the new Flash based View portal. Some new features in ESX 4.1 too, like working host USB redirection.